



Consulting: strategy aligned to your business
Roadmaps, governance and GRC frameworks that align leadership, risk, and investment priorities.
StrategyGovernanceGRC
We turn regulatory complexity and cyber risk into clear, measurable readiness.

Security is not just defense. It is how organizations grow with confidence.
Roadmaps, governance and GRC frameworks that align leadership, risk, and investment priorities.
Rigorous audits and testing that reveal control weaknesses, compliance gaps, and what to fix first.
Automating security, compliance, and operational processes so readiness never slips.
A resilient cybersecurity program that protects your people, data, and operations.
Roadmaps that align leadership, risk, and investment priorities across the business.
We listen first, then map the business and security reality.
We leave your team with practical tools, decisions, and confidence.
Cybersecurity strategy, program design, maturity assessments and awareness programs that turn risk into clear priorities.
Security, technical and ISO compliance audits, risk assessments and control reviews that show exactly what to fix first.
AI and automation advisory, technology integration and security automation that keep controls and compliance running.
Penetration testing, red teaming, threat intelligence, incident response and digital forensics that protect people, data and operations.
Leadership teams need security-conscious AI strategies that create momentum without creating regulatory risk.
When teams can see what matters, they can reduce noise and prioritize the risks that truly affect business continuity.
The right controls do more than reduce risk. They enable faster decisions, better partnering, and smoother delivery.
Modern organizations need a practical roadmap to convert digital ambition into safe, measurable business progress.
Practical guidance and strategic perspectives to help organizations navigate risk, resilience, and digital transformation.
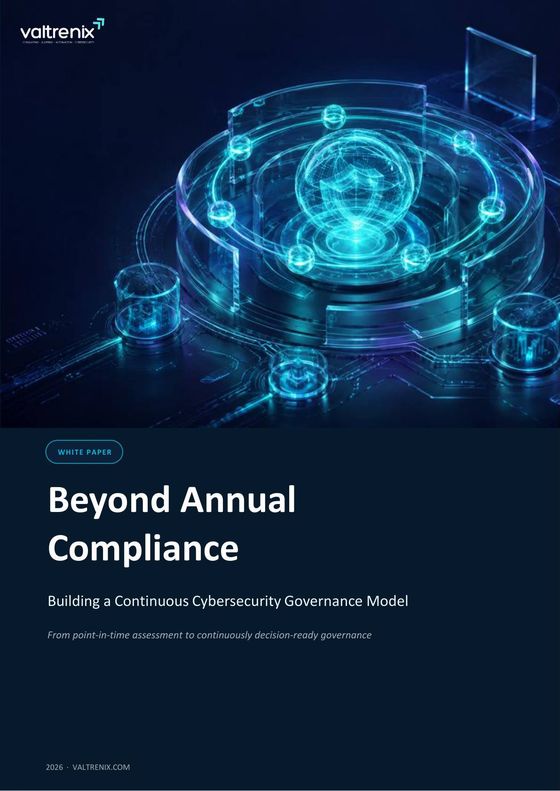
Annual assessments capture a moment in time. Meanwhile, people change roles, vendors are added, systems evolve, and evidence grows stale. This Valtrenix whitepaper shows how to keep cybersecurity governance current between assessments, so leaders can see what changed, who owns the risk, and what decision is needed.

AI agents can do more than generate answers. They can use credentials, access data, call tools and change real systems. That ability creates operational risks that require clear ownership and controls over what each agent is allowed to do. This Valtrenix whitepaper explores how organizations can assess agent use cases and govern autonomous actions. Its frameworks and controls are illustrative concepts for learning and discussion.
A new research perspective is on its way. Check back soon for the next Valtrenix whitepaper.
Valtrenix helps leaders see what changed between assessments, who owns the risk, and what decision is needed.
Whether you need strategic guidance, assurance support, or a resilient security framework, our team is ready to help you move forward with clarity.
